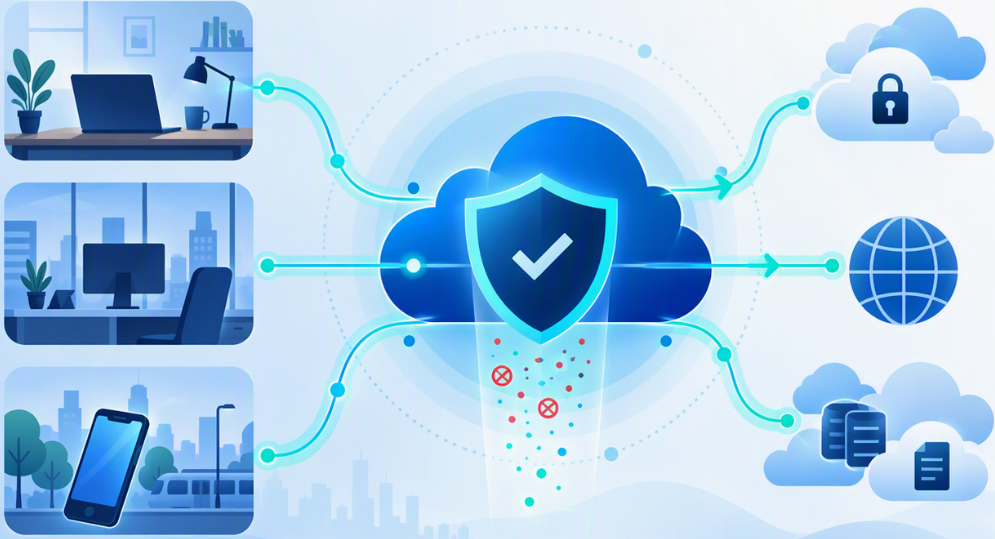
A Secure Web Gateway (SWG) is a security solution that inspects and controls web and cloud traffic, so users stay protected wherever they connect. Work no longer happens in one place. Employees connect from home, branch offices, and while travelling, and most of what they do runs through the browser and cloud apps. Traditional perimeter security was designed around a central office network, so it loses visibility when traffic never passes through one.
A Secure Web Gateway built on zero trust principles brings that visibility back. Platforms such as Zscaler Internet Access, Cloudflare One, and Netskope Next Gen SWG inspect and control web traffic wherever users connect, without routing it through a data center.
Top Secure Web Gateway Platforms and Their Strengths
Each platform delivers SWG and zero trust, but each leads with something different.
1. Zscaler Internet Access (ZIA): Built for Scale
ZIA is a cloud-native platform with zero-trust access, SSL inspection, CASB, and AI-driven threat detection. A market leader in SWG, it suits large enterprises with hybrid workforces. Deployment can be complex, so planning matters.
2. Cloudflare One: Built for Speed and Simplicity
Cloudflare One brings SWG, DNS filtering, browser isolation, and zero trust together on its edge network. It is easy to deploy and works for both SMBs and enterprises. Very large environments may find its granular reporting limited.
3. Netskope Next Gen SWG: Built Around the Data
Netskope puts data protection first, with ML-based threat detection, DLP, and granular URL and app filtering. It suits cloud-first organizations that need strong zero trust enforcement around sensitive information. Expect a steeper learning curve during configuration.
Security Risks Without Secure Web Gateway Protection
Missing this layer rarely causes an immediate failure. It creates quiet gaps that build over time:
- Threats inside encrypted traffic: Without SSL inspection, malware and phishing can pass through HTTPS unnoticed.
- Data leaving unseen: Sensitive files can be uploaded to unsanctioned apps and personal cloud storage with no control.
- Uneven protection: Remote users and branch offices often receive weaker controls than head-office staff.
- Audit challenges: Missing access logs and unenforced policies are hard to defend in audits and customer security reviews.
How to Implement Zero Trust Web Security in 5 Steps
- Map access. Understand how users, devices, and locations reach web and cloud apps, and where sensitive data flows.
- Set the rules. Define policies for URL and app access, data handling, and device posture based on least privilege.
- Choose the right fit. Match a platform to your size, workforce model, in-house skills, and reporting needs.
- Pilot first. Start with a small user group, tune policies, then expand in phases.
- Review continuously. Check threat and usage reports regularly and adjust as your environment changes.
Secure Web Access Without the Friction
Zero trust does not have to slow people down. When every connection is verified and policies apply consistently, users get dependable access from anywhere and security teams gain clear visibility.
As hybrid work and cloud adoption grow, the gap between organizations with modern web security and those relying on legacy perimeters will keep widening. Whether you begin with Zscaler, Cloudflare One, Netskope, or a focused pilot, the first step is the same: understand how your users reach the web, and make sure every connection is inspected and under control.